 Live
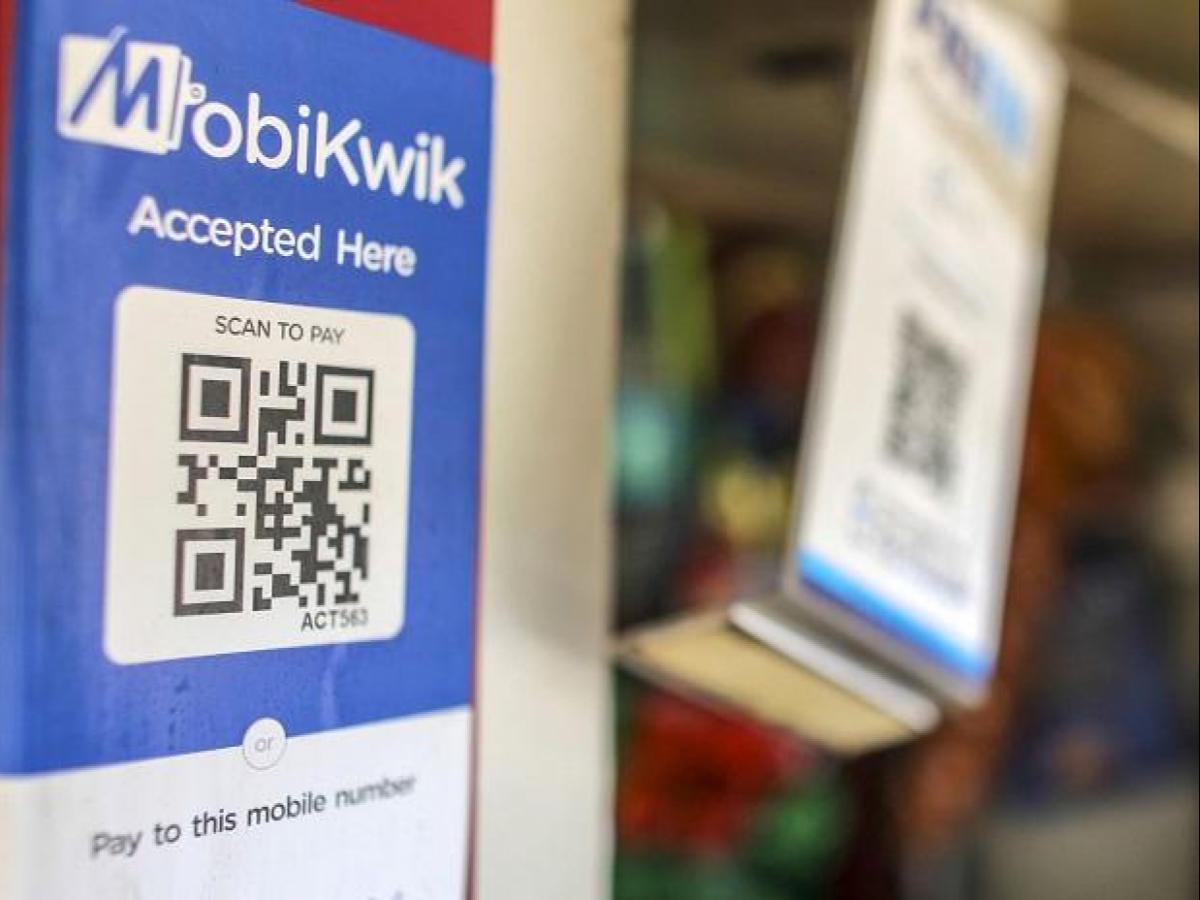
Digital wallet and payments company MobiKwik, reportedly planning an initial public offering (IPO) around September this year to raise $200-250 million, on Monday denied claims that sensitive data of millions of its users has been leaked. Independent cybersecurity researchers have claimed that a database containing KYC details of nearly 3.5 million users of MobiKwik is up for sale on the Dark Web.
First tweeted by independent cybersecurity researcher Rajshekhar Rajaharia and then by French researcher Elliot Alderson on Monday, the alleged breach includes 8.2TB data containing users’ phone numbers, emails, hashed passwords, addresses, bank accounts, and card details. MobiKwik, however, vehemently denied any such breach.
“Some media-crazed so-called security researchers have repeatedly attempted to present concocted files wasting precious time of our organization as well as members of the media,” the company said in a statement shared with IANS. “We thoroughly investigated and did not find any security lapses. Our user and company data is completely safe and secure,” the company added.
- Technocraft Industries Hits Day High, Q2 Revenue Up 29%
- InCred Capital Acquires Quintessentially India to Expand Services
- Ola Fined Rs 10 Lakh Over Advance Tip Prompts for Rides
- Tata Motors PV Posts Rs 5,531 Cr Q2 Loss on JLR Costs
- Kanoria Chemicals Hits Day High as Q2 Profit Jumps 258%
Rajaharia had claimed earlier that “11 crore Indian cardholder’s cards’ data including personal details and KYC soft copy (PAN, Aadhaar, etc) allegedly leaked from the company’s server in India”. According to the researchers, the entire database is available for nearly $84,000 on the Dark Web. The reports surfaced as MobiKwik last week raised $7.2 million in a funding round prior to the listing on the stock exchange, according to regulatory filings with the Ministry of Corporate Affairs.